End-to-end encrypted · No metadata · Resistant to forensic analysis · For the toughest requirements
Every message, every call, every file: encrypted before leaving your device. And above all — nothing remains on the device! No metadata. No data traces. Resistant to forensic analysis.
When logged out, no content data are available on the device — losing it would not matter, and no remote wipe is needed.
With MDM systems, remote wiping and access controls always depend on the wipe command still reaching the device. That is not the case with what we offer.
If you block a participant, even temporarily, neither that participant nor anyone else can force access.
Available on multiple devices without scattering and duplicating data across them.
Every threat has an architectural answer — beyond a promise.
End-to-end encryption with cryptographic parameters exceeding Top Secret requirements — only ciphertext exists in transit.
Who communicates with whom, when and how often — often more revealing than the content. No analysable metadata are generated here.
No content on the device, nothing to extract forensically. A lost or seized device reveals nothing.
Communications intercepted today remain unreadable even to future quantum computers — post-quantum cryptography is fully implemented.
Zero-knowledge architecture: even server administrators, including ICSL's, cannot decrypt content.
If your normal IT is compromised, the solution continues communicating independently — through to dedicated Crisis Backup.
Calls, messages and files are encrypted on your device — plaintext content exists only with you.
The server relays only ciphertext. It cannot read it — and never needs to. That is precisely why the same infrastructure is approved for government use.
Only the authorised recipient can read the content. After logout, what remains on the device is: nothing.
A board member travelling: unfamiliar networks, foreign countries — the connection remains secure and the device stays clean, even at a border inspection.
Government agencies and armed forces: approved for classified use on commercially available iOS, Android and Windows devices.
Law firms, trustees, supervisory board members: client and business secrets without data traces — available immediately as a service.
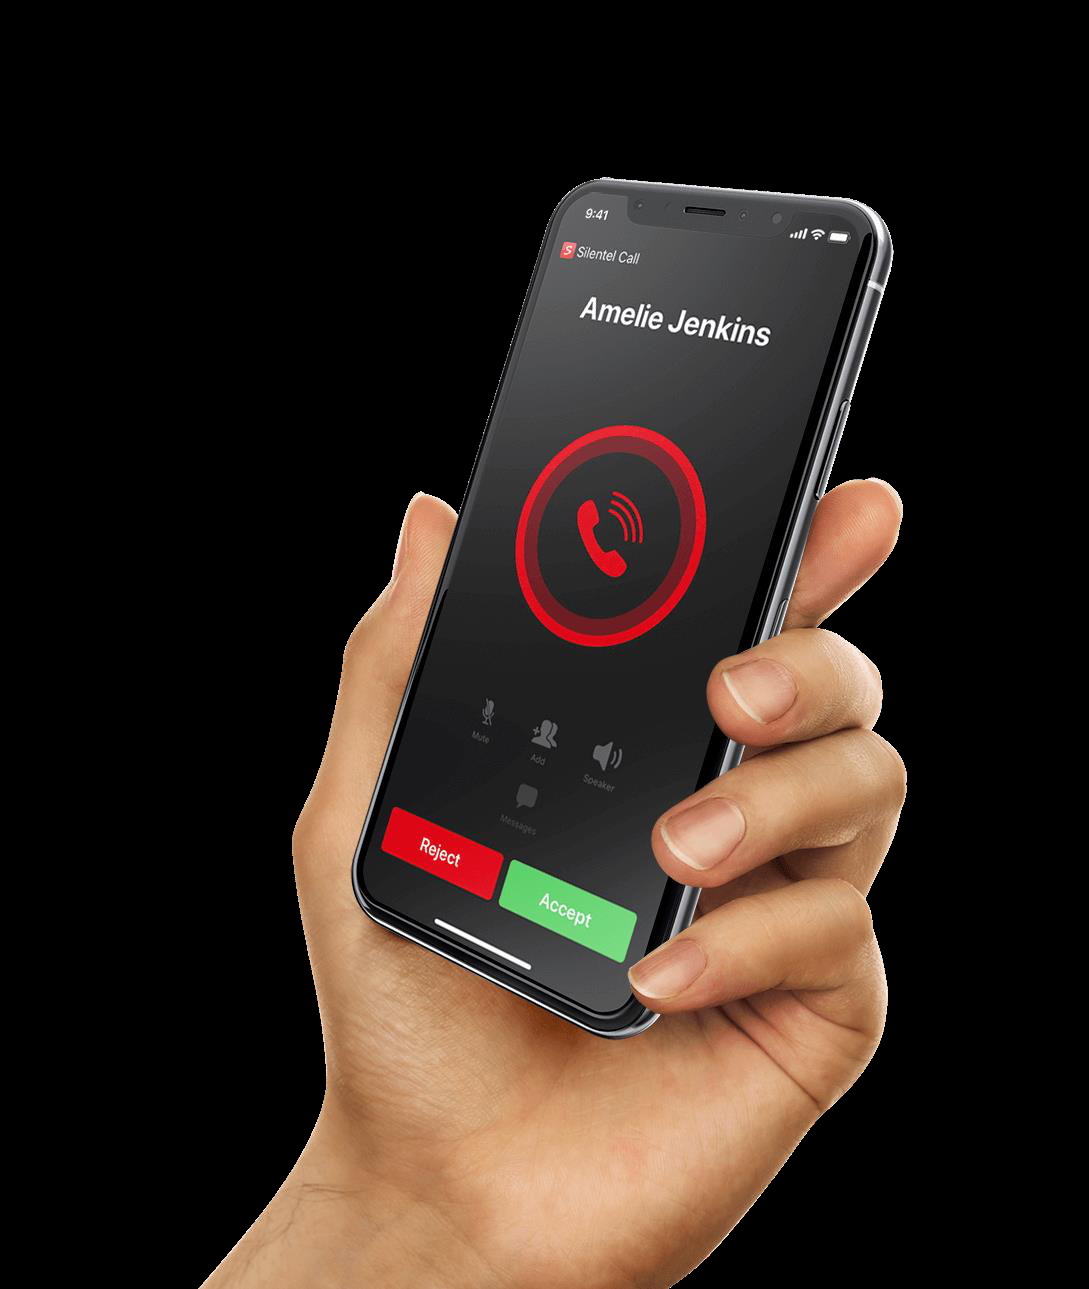
No. The solution runs on commercially available iOS, Android and Windows devices — approved for classified use. For particularly demanding requirements, there are also Custom Devices.
Only if you want to. From as-a-Service (active the same day) through Hosted to On-Premise — compare all deployment models.
Nothing. No content data are stored on the device — no data loss, no remote wipe needed, no forensic analysis possible.
No. Data and voice are never available unencrypted — even to administrators. That is why ICSL operates the same infrastructure for government and private customers.
With Silentel as-a-Service Premium the same day — available anonymously, without your own backend. On-Premise typically within 2–4 weeks.
Arrange a confidential briefing. We will analyse your current communications situation and show you practical options.